In brief
1) Minnesota reported a coordinated attack on more than 30 state water systems, and the FBI says attacks have spread to seven states. 2) U.S. cybersecurity agencies suspect an Iranian cyber‑group, dubbed Handala, behind the strikes. 3) The real danger lies in eroding public trust in clean water, though future attacks could threaten actual supplies. 4) CISA urges immediate upgrades and removing vulnerable systems from the internet to protect water infrastructure.
Last week the state of Minnesota announced that more than 30 of its water systems had been hit by a coordinated cyber‑attack. Soon after, the FBI confirmed that similar hacks have affected seven U.S. states and that some water operations were degraded in the process.
Cyber‑security agencies now suspect the Iranian government’s cyber‑group, Handala, behind the strikes. Although the U.S. President has not publicly blamed Iran, experts say Tehran would likely be involved because of its history of targeting U.S. infrastructure.
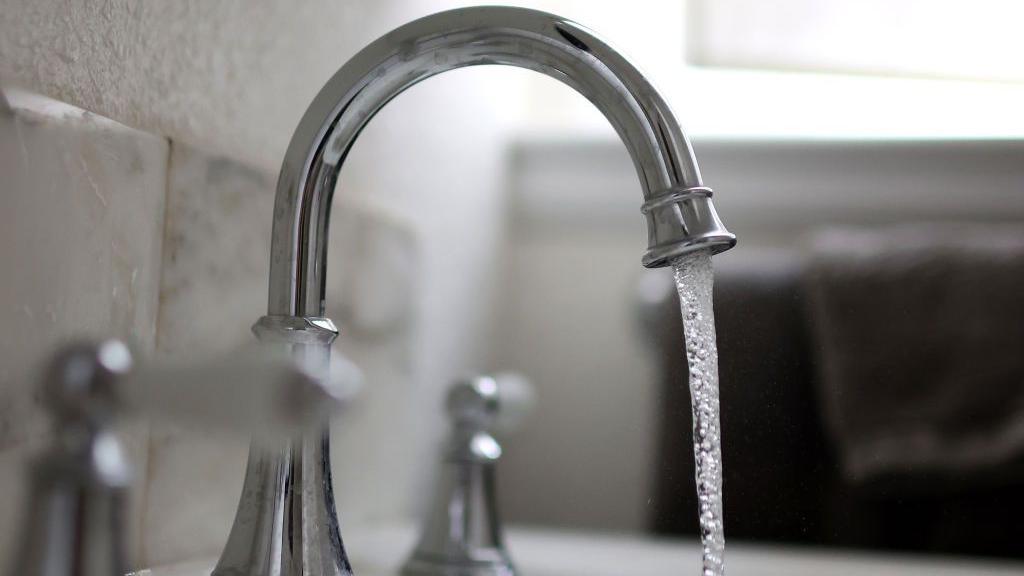
Why is this a problem? The attack threatens not just the water itself, but the confidence people have in receiving safe drinking water. If people start doubting whether the tap is safe, it could create a crisis of trust across the country.
And what can be done? CISA and the U.S. Environmental Protection Agency have issued guidance that urges water utilities to upgrade security, move devices off the internet, and reset passwords immediately.
A Timeline of Known Iranian‑Linked Hacks
- 2026 – Handala disrupted a medical tech firm, leaking sensitive data.
- 2024 – Iranian actors hacked U.S. political campaigns to sow discord.
- 2023 – Water and wastewater systems in Pennsylvania were attacked by a group linked to the IRGC.
- 2020 – Two Iranian nationals were charged for targeting voter data in the U.S. election.
- 2017 – Ransomware attacks targeted local governments and healthcare institutions.
For more on Handala’s history, check out the U.S. Justice Department’s disclosure.
How Could We Keep the Water Safe?
Most U.S. water utilities are publicly run and depend on aging technology. Without upgrades, the nation faces a serious security risk.
CISA recommends:
- Move critical control systems offline from the internet.
- Perform immediate password resets.
- Upgrade legacy equipment with modern security protocols.
- Collaborate with federal agencies for ongoing threat updates.
The bottom line: While the hacks didn't yet taste bad water, the possibility of malicious chemicals or shut‑offs still looms. Time for a nationwide upgrade.
Source: BBC News (2026-08-04) – accessed via the original article.